Why offboarding fails more often than launches
Switching web hosts, agencies, or freelancers should feel like a controlled handoff—not a scramble after DNS stops resolving. The messy part is rarely the new build. It is the invisible inventory: who owns the registrar, which mailbox gets renewals, whether Search Console still lists a departed contractor, and whether staging still holds production credentials.
This is a practical offboarding checklist TwoQM uses when small businesses leave or change a website, hosting, or digital-vendor relationship—not a vendor roast. Treat it as the day-before-cutover worksheet.
Most “we moved hosts and everything broke” stories share one root cause: access lived in one person’s head—shared passwords, agency-owned domains, analytics under a personal Gmail, invoices auto-charging a card you cannot see. Offboarding makes that stack visible, then reclaiming or rotating every piece before you cancel. After access is cut, recovery gets slower and more expensive.
Step 1: Inventory the full stack (not just the website)
Open a shared sheet and name a company owner for every row. Minimum columns: service, URL/login, who owns it today, who should own it after exit, credentials recovered?, billing moved?, notes. Walk these categories:
Domain registrar — Where the domain renews, locks, and transfers. Confirm the account email and phone are yours, not the vendor’s.
DNS host — Registrar DNS, Cloudflare, Route 53, or the host’s nameservers. Export a full record list (A, AAAA, CNAME, MX, TXT, SPF/DKIM/DMARC).
Web hosting / VPS / cloud — Control panel, SSH keys, SFTP users, deploy tokens, and any CDN in front of the origin.
CMS admins — WordPress, Webflow, Shopify, Squarespace—every Administrator / Owner seat, including “temporary” agency logins.
Email and mail DNS — Microsoft 365, Google Workspace, or host email. Confirm MX and authentication records will still match after DNS moves.
SSL / certificates — Auto-renew paths (Let’s Encrypt via host, Cloudflare, or a purchased cert). Note expiry and who can reissue.
Backups and staging — Where daily/weekly backups live, how to restore, and whether staging shares production secrets.
Analytics and Search Console — GA4 (or equivalent), Google Search Console, Bing Webmaster—property ownership, not just “view” access.
Google Business Profile — Managers and owners for the business listing tied to your site.
Invoices, contracts, and renewals — Auto-pay cards, annual retainers, domain privacy add-ons, and who gets the renewal email.
Blank rows are risks.
Step 2: Reclaim ownership before you rotate anything
Access without ownership is a lease. Before you change passwords:
Transfer domain admin to a company-controlled registrar login (or confirm you already have it).
Move hosting billing and root/org ownership to a mailbox your team monitors.
Add your people as Owners in Search Console, Analytics, and Google Business Profile; remove vendor-only ownership where the platform allows.
Download exportable assets: site files, database dumps, media libraries, theme/plugin lists, DNS zone files, SSL certs if you hold them, and a content inventory.
Collect documentation: how deploys work, custom redirects, cron jobs, forms destinations, and third-party integrations (chat, payments, booking).
Ask for a written list of every account the vendor created “for convenience.”
Step 3: Remove shared passwords and rotate credentials
Once you hold Owner seats, rotate:
Registrar, DNS, hosting, CMS, email admin, CDN, backup vault, and staging.
API keys, deploy keys, webhook secrets, and “app passwords.”
Any shared admin@ / info@ password that lived in a Slack pin or a PDF titled “logins.”
Prefer named user accounts with roles over one shared superuser. Turn on MFA for every login that can change DNS, hosting, CMS, or email, and store recovery codes offline—not in the vendor’s old chat history.
Revoke vendor seats after your team can log in and restore from backup—not before you have the database dump.
Step 4: Confirm who can renew—and who gets the bill
Offboarding is unfinished if renewals still surprise you:
Domain auto-renew on, correct card, and lock enabled.
Hosting and SSL renewal emails going to a monitored company address.
Cancel or transfer vendor retainers and unused seats so you are not paying for ghost access.
Note contract end dates, notice periods, and any “data hold” or export fees in writing.
Name renewal owners on the sheet—domains expire on holiday weekends when nobody owns the reminder.
Step 5: Document recovery contacts and a 30-day hypercare plan
Write a one-page runbook:
Primary and backup technical contacts inside your company.
Registrar support path and account PIN if required.
Host and DNS support contacts for the new stack.
Where backups live and the last successful restore test date.
Who can approve emergency DNS or MX changes.
For 30 days after cutover, watch DNS, forms, email deliverability, SSL, and Search Console. Keep the old host on a read-only or paid hold until you complete a restore drill on the new side—if the contract allows.
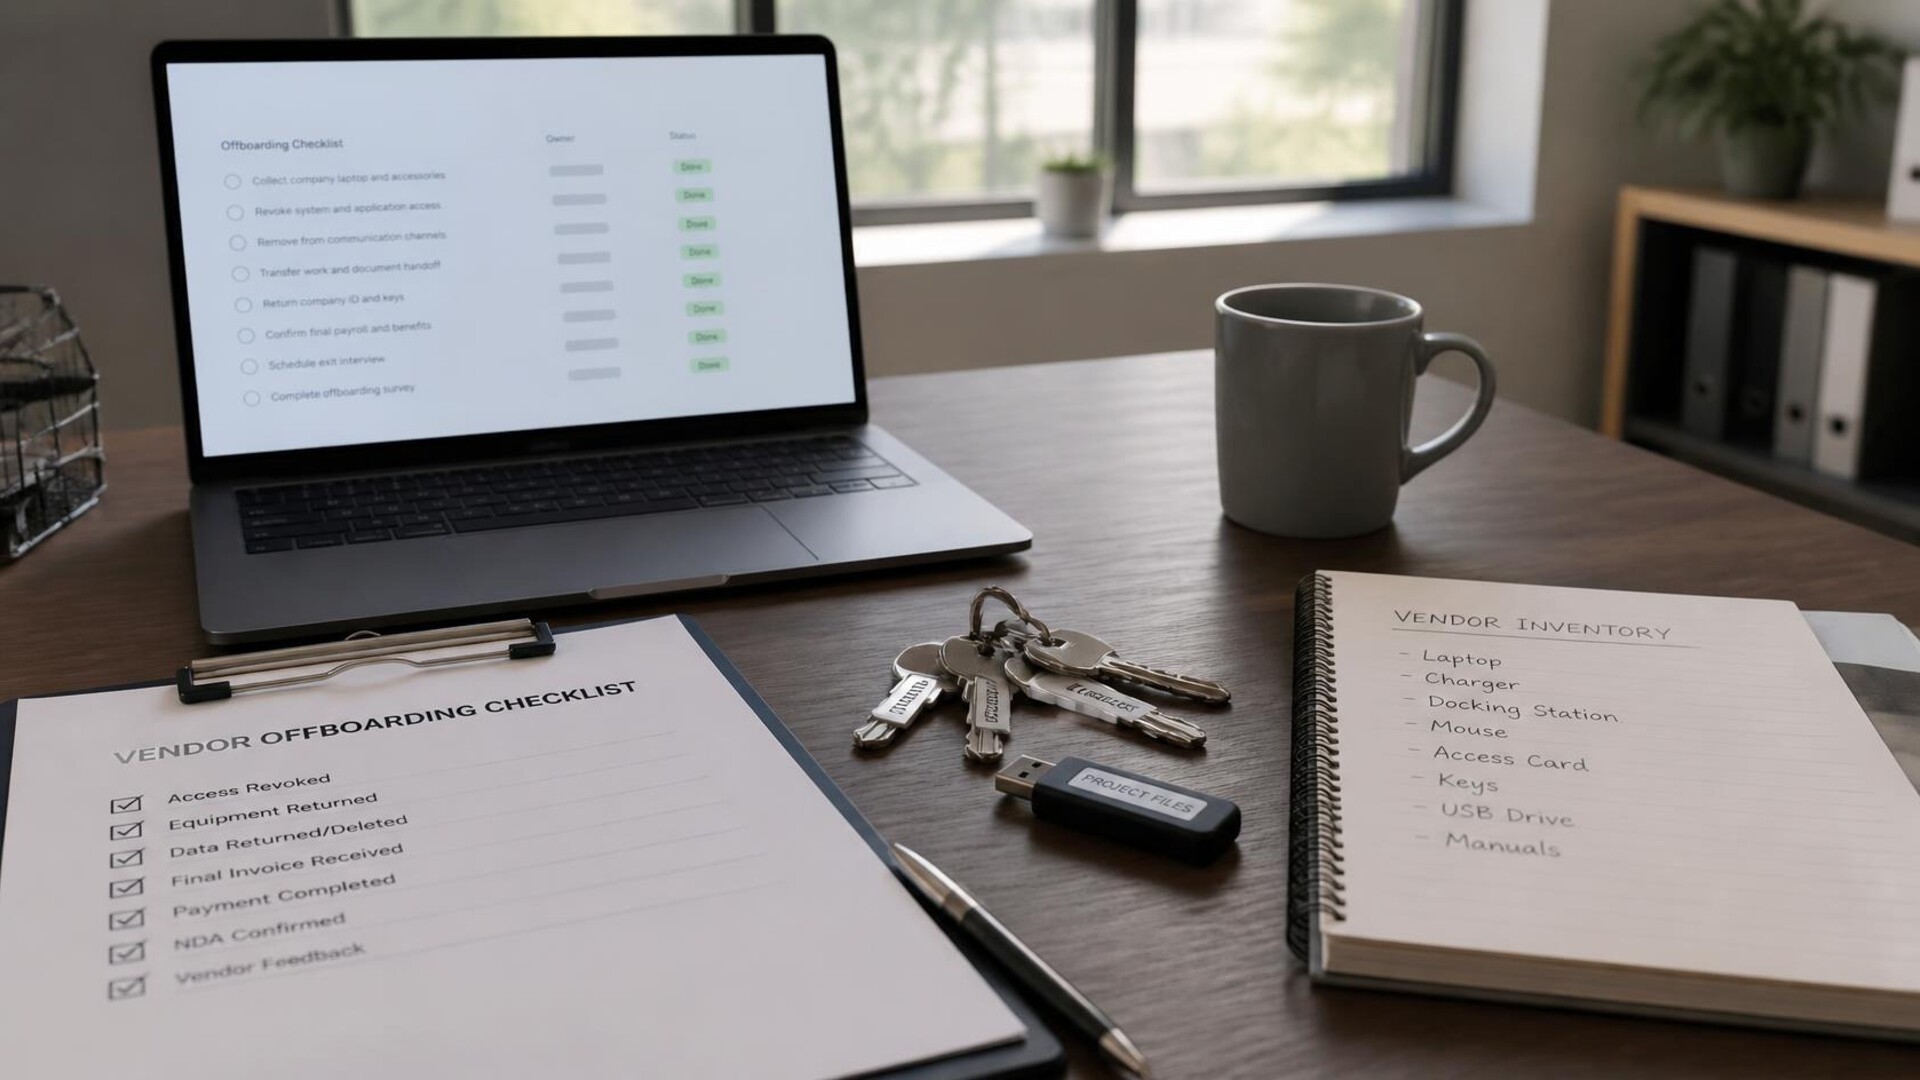
A short offboarding checklist
Full inventory sheet with named company owners
DNS zone export + email auth records verified
Domain, hosting, CMS, Analytics, Search Console, GBP ownership reclaimed
Site files, database, media, and backup restore path in your hands
Vendor seats removed; credentials rotated; MFA on
Billing and renewal contacts on company mailboxes
Recovery contacts and 30-day watch list written down
How TwoQM thinks about vendor exits
We help businesses run websites, hosting, and day-to-day digital support without mystery access. A clean offboarding matches a clean launch: inventory, ownership, backups, credentials, renewals—on paper—before deadlines take over.
If you are changing hosts or parting ways with a web vendor and want a second set of eyes on the checklist, reach out to TwoQM. We will keep it practical: what you must hold, what you can cancel, and what to verify before the old login stops working.